CHAPTER 6
What is Human-in-the-Loop? AI Governance & Security
By this point, you’ve learned how to build, ground, deploy, and orchestrate generative AI systems. The final step is ensuring they remain safe, governed, and trustworthy in production.
This raises an important question: What is Human-in-the-Loop? HITL is the practice of keeping people involved in AI-driven decisions whenever accuracy, compliance, or accountability matter.
It’s easy to assume that scaling AI simply means: bigger models, more data, more automation.
In practice, mature AI programs face three challenges:
- Operational fragility: systems that work in a demo collapse under real-world load.
- Governance gaps: sensitive data slips into prompts, logs, or vector indexes.
- Accountability voids: no clear ownership when AI produces harmful or incorrect outputs.
These problems are not technical at the model level; they are systemic. The solution is not bigger infrastructure, but safer infrastructure.
In this chapter, you’ll learn how to:
- Understand what Human-in-the-Loop is and when to apply it.
- Evaluate AI systems for quality, safety, and reliability.
- Build governance frameworks for enterprise AI.
- Protect AI systems with security and compliance best practices.
Human-in-the-Loop: The Foundation of Trust
Once a system begins generating content that influences real decisions, humans must remain the ultimate checkpoint.
Human-in-the-Loop is an intentional design principle that makes automation auditable, safe, and compliant.
Why HITL Matters
LLMs and AI agents can accelerate workflows dramatically, but no model is perfect. And no regulator will accept “the AI said so” as justification for an action.
HITL ensures:
- Humans validate outputs
- Risky decisions are escalated
- Errors are intercepted before they propagate
- Accountability remains intact
Where HITL Is Essential
- Healthcare: doctors approve AI-generated summaries before archiving to EHR
- Finance: analysts validate risk classifications and compliance reports
- Legal: attorneys review contract drafts and redlines
- Customer service: supervisors review escalations or ambiguous queries
HITL is the guardrail that lets automation expand without compromising safety.
Once Human-in-the-Loop is in place, the next step is evaluating models before they reach production.
HITL Patterns: Balancing Risk, Speed, and Cost
In practice, HITL is not a binary “yes or no” choice. Mature enterprises design their workflows around three distinct patterns, each carrying different operational implications:
How to Validate and Evaluate an AI Model to Prove that Is Ready?
Before deployment, models (LLMs, RAG pipelines, and agents) must pass rigorous validation workflows.
This evaluation serves two primary goals:
- Ensure technical quality (accuracy, grounding, robustness)
- Demonstrate compliance (ethics, safety, fairness)
| Pattern | How it Works | Use Case Example | Risk vs. Speed Trade-off |
|---|---|---|---|
| Human-in-the-Loop | Blocking Checkpoint: The system pauses and waits for explicit human approval before the action is executed. | High-value wire transfers; medical prescriptions. | Maximum Safety / Lower Speed. Prevents errors but creates bottlenecks. |
| Human-on-the-Loop | Asynchronous Monitoring: The system acts autonomously, but a human reviews the logs or actions after the fact to intervene if necessary. | Low-risk customer service emails; content moderation at scale. | High Speed / Managed Risk. Ideal for high-volume tasks where mistakes are reversible. |
| Human-as-the-loop | AI-Assisted Human: The human remains the sole decision-maker; the AI only provides research, drafts, or context. | Legal contract drafting; complex strategic planning. | Human-Led Accuracy. AI acts as a co-pilot, not an autopilot. |
Core Evaluation Dimensions
- Accuracy and factual grounding: Is the model correct?
- Bias and fairness: Do outputs behave consistently across users?
- Robustness: Does it withstand adversarial prompts or noise?
- Policy alignment: Does it comply with internal governance and legal standards?
Common Frameworks and Evaluation Approaches
To move beyond “vibes-based” testing, enterprises adopt systematic evaluation workflows that provide hard metrics on model performance:
- LLM-as-a-Judge: Using high-reasoning frontier models to automatically score the outputs of production pipelines based on custom rubrics (tone, accuracy, policy compliance).
- Custom Enterprise Audit Datasets: Curated "Gold Datasets" of real-world prompts and their ideal "ground truth" answers, aligned with internal policies and domain knowledge.
- Agent Behavior Simulations: Running agents through "sandbox" scenarios to validate their decision paths and tool usage before they touch live data.
However, when Retrieval-Augmented Generation is involved, generic evaluation is not enough.
RAG systems fail in subtle ways: retrieving the wrong context, using partial information, or generating answers that sound confident but are not grounded.
For this reason, enterprises increasingly adopt RAG-specific evaluation frameworks such as RAGAS and TruLens, which are designed to measure how well a system retrieves, uses, and respects its context.
- RAGAS focuses on evaluating the quality of retrieval and grounding by scoring metrics like context precision, recall, and faithfulness across RAG pipelines.
- TruLens (now part of Snowflake’s AI ecosystem as TruLens Eval) provides end-to-end observability and evaluation for LLM applications. It helps teams trace how retrieved context influences final answers and detect hallucinations or grounding failures in production.
What Are The Key RAG Evaluation Metrics?
- Context Precision: Are the retrieved documents actually relevant to the question?
- Context Recall: Did the system retrieve all the information needed to answer correctly?
- Faithfulness: Is the answer grounded strictly in the retrieved context, without hallucination?
- Answer Relevance: Does the final response actually address the user’s question?
These metrics shift evaluation from “does the answer sound good?” to “can we trust how the answer was produced?”
AI Governance and Compliance: How to Build Safe AI
As AI becomes embedded in customer interactions, workflows, and operations, governance and regulation become unavoidable.
SOC 2, HIPAA, GDPR, and CCPA all include expectations for how AI processes data, logs interactions, and preserves privacy.
The EU AI Act also introduces a risk-based classification framework specifically for AI systems.
It categorizes them as minimal, limited, high-risk, or unacceptable risk, with compliance obligations ranging from transparency requirements to mandatory human oversight for high-risk applications (healthcare, finance, hiring, critical infrastructure).
Governance is not bureaucracy. It is how enterprises answer the question:
“If something goes wrong, can we prove what happened, why, and who approved it?”
Key Governance Components
Audit Logs
Track:
- Who prompted what
- When the output was generated
- Where the data came from
- Which model was used
Explainability
Executives and regulators must understand:
- How the system made its decision
- What inputs influenced it
- Whether sensitive data was involved
Role-Based Access Control (RBAC)
Separate responsibilities:
- Developers (build)
- Reviewers (validate)
- Auditors (oversee & report)
Governance defines who sees what, who approves what, and who is accountable. Even with governance in place, AI systems face one more category of risk: security.
AI Security: Protecting AI Systems
Generative AI introduces attack surfaces that did not exist in traditional software.
Prompt injection, data leakage, model manipulation, and unsafe tool calls are increasingly exploited in the wild.
Common AI-Specific Attacks
- Prompt Injection: tricking the model into breaking rules
- Data Leakage: exposing sensitive data via outputs
- Unauthorized Tool Calls: agents executing unintended actions
- RAG Poisoning (Indirect Prompt Injection): injecting malicious content into the knowledge base to manipulate retrieved answers.
Mitigations: Protecting the AI Perimeter
Security ensures AI actions remain safe and predictable. To protect the enterprise, engineering teams must implement a multi-layered defense strategy:
- Input Filtering and Sanitization: Neutralizing malicious instructions (prompt injections) before they reach the model.
- Output Moderation: Automated scanning of AI responses to prevent the leakage of PII or off-brand content.
- Sandboxed Tool Execution: Running agent actions in isolated environments (like Docker containers) to prevent unauthorized system access.
- Least-Privilege API Permissions: Granting agents access only to the specific data and tools required for their task, nothing more.
- Rate Limiting and Anomaly Detection: Monitoring for unusual patterns, such as an agent making 1,000 requests in a minute, to stop runaway costs or attacks.
- Red-Teaming and Adversarial Evaluation: Simulating attacks to find vulnerabilities in the model's logic before a malicious actor does.
Once Human-in-the-Loop, evaluation, governance, and security are in place, leaders can confidently scale AI across use cases.
Security in the age of LLMs is about governing intent.
To help your team visualize the necessary guardrails for a production-grade system, download The Enterprise AI Governance & Security Blueprint.
A technical map that outlines the four layers of defense required to protect your data, your brand, and your users from emerging AI threats.
AI Governance & Security Blueprint
Free DownloadHuman-in-the-Loop Decision Framework
To help leaders choose the right level of human oversight for each AI use case, this playbook includes a simplified decision matrix:
| Enterprise Goal | Recommended Practice | Avoid When |
|---|---|---|
| Improve output reliability | HITL review before publishing | If ultra-low latency (<1 sec) is required |
| Ensure compliance | Governance with audit trails | If data is fully public |
| Reduce security risk | Input/output sanitization | Never skip for customer-facing systems |
| Scale AI teams | Clear ownership roles | Avoid unclear accountability |
Decision frameworks give enterprises consistency. The next section illustrates these principles through real-world examples.
Real-World Scenario: Human-Validated Compliance Reporting
The Challenge: A multinational bank needed to automate weekly compliance summaries.
The stakes were high: the system handled sensitive PII, required strict regulatory alignment, and allowed zero margin for error.
Secure and Compliant Architecture: To solve this, we designed a system that balances speed with enterprise-grade control:
- Intelligence: Frontier Model (via Azure OpenAI) for high-reasoning synthesis.
- Memory: RAG for factual grounding.
- Security: Document-level RBAC on the vector store (e.g., Pinecone namespaces or Weaviate tenants) to ensure the AI only retrieves documents the specific user is authorized to see.
- Observability: LangSmith for end-to-end trace auditing.
- Checkpoint: A custom Internal Approval Dashboard for the final Human-in-the-Loop (HITL) sign-off.
The Workflow:
- Ingest: Data is retrieved respecting user-level permissions.
- Draft: AI generates a summary grounded in verified facts.
- Audit: System logs every reasoning step for compliance.
- Approve: A compliance analyst reviews, edits, and signs off.
Business Outcome:
- Efficiency: 70% reduction in reporting time.
- Risk: Zero compliance incidents.
- Trust: Full auditability and transparency for regulators.
Scenarios like this illustrate the chapter’s central idea: scaling AI is about empowering humans while ensuring enterprise-level control, not about replacing them.
Leader’s Lens: Questions Every Executive Must Answer
To assess whether your AI systems are truly ready to scale, ask the following:
- Who validates AI outputs before they affect customers?
- Are decisions, prompts, and actions logged and traceable?
- What is the escalation path when AI and humans disagree?
- Who owns the fix when something breaks: Engineering, Product, Data, or Compliance?
- Can we defend our AI processes to auditors or regulators tomorrow?
If leaders cannot answer these questions confidently, the system is not enterprise-ready, regardless of how impressive the underlying model is.
How to Avoid Common AI Governance Pitfalls
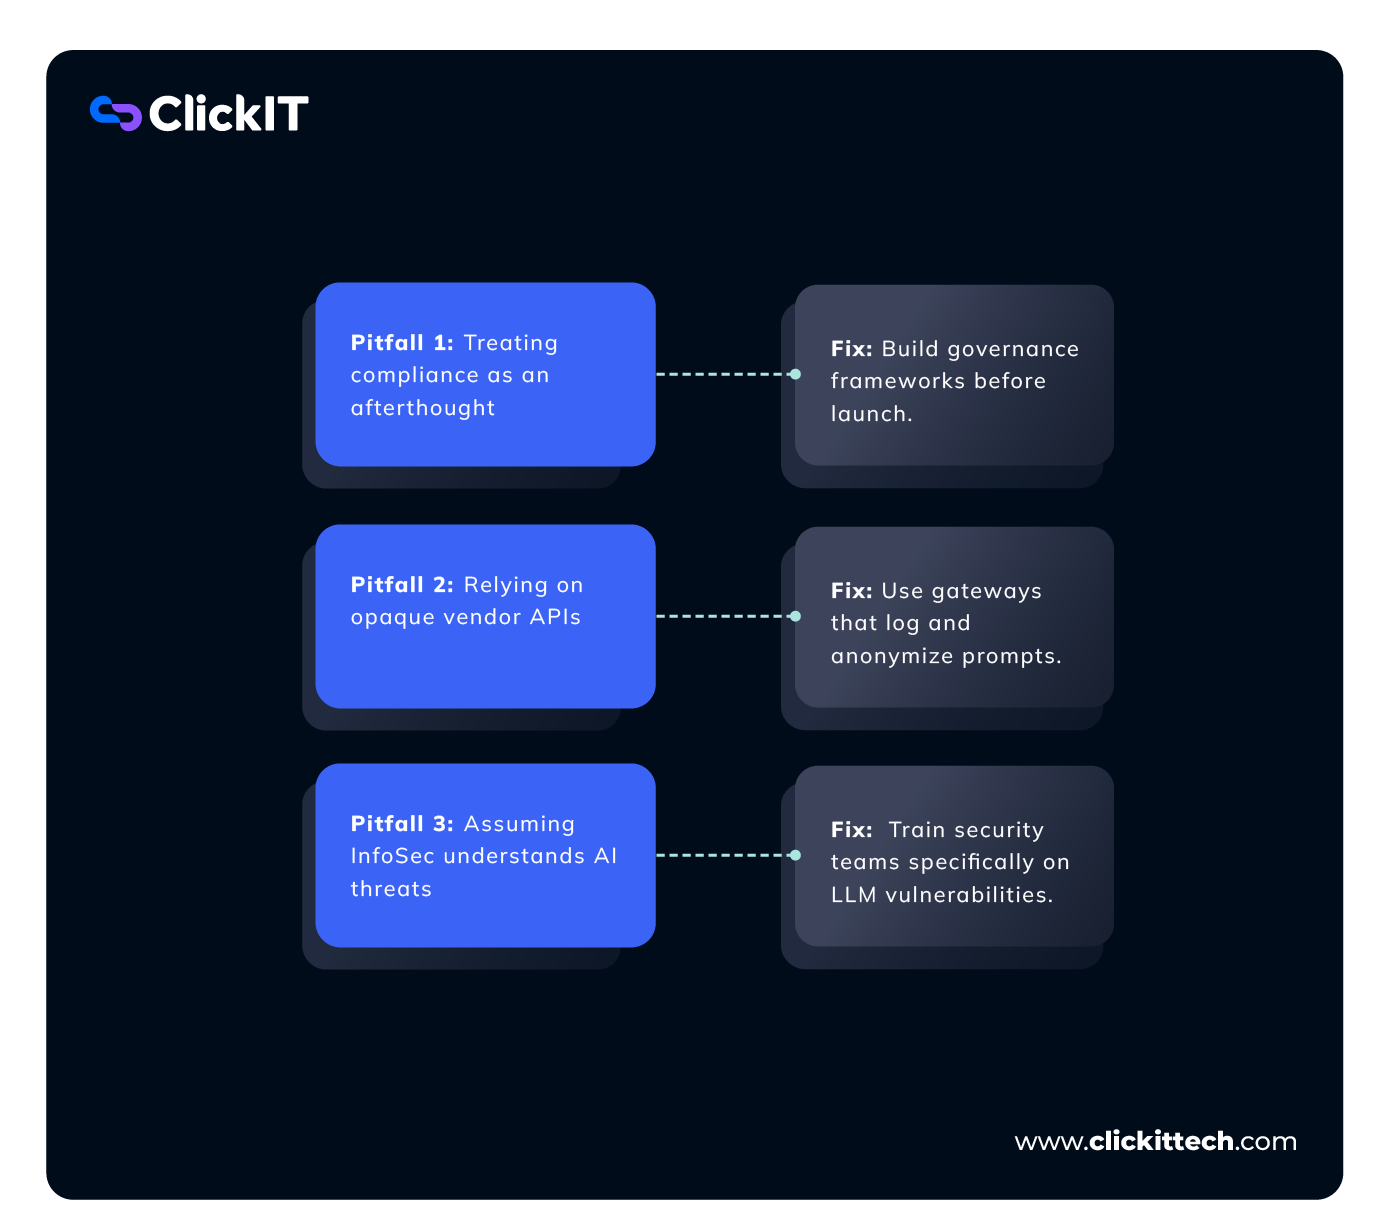
AI Governance Action Checklist
- Conduct an AI audit for traceability gaps
- Define HITL workflows for high-impact decisions
- Integrate LLM monitoring into SOC 2 / ISO 27001
- Red-team AI systems quarterly
- Publish an internal AI Governance Charter
- Train all AI stakeholders on responsible use
No AI Governance, No Growth
Human-in-the-Loop, governance, and security aren’t limitations. They’re accelerators of trust.
They allow enterprises to scale generative AI confidently, satisfy regulators, and maintain the trust of customers, partners, and employees.
In short:
Powerful systems require powerful guardrails.
Without governance, AI stalls.
With governance, AI scales.
Conclusion: Trust Your Enterprise AI
Throughout this journey, we have explored the building blocks of enterprise AI; from reasoning and RAG to agentic systems and LLMOps.
But as we have seen in this chapter, even the most sophisticated architecture is only as strong as its governance.
Security, human oversight, and systematic evaluation are what allow your organization to transition from experimental AI to an AI-First Enterprise.
What’s Next? Building the system is the beginning. Sustaining it, evolving it, and capturing long-term value is the mission.
In Chapter 7: The Path to the AI-First Enterprise, we will provide a strategic roadmap to unify these technical pillars into a cohesive business strategy.
And also a curated library of resources and frameworks to accelerate your deployment today.
Ready to bring it all together? Let’s continue to the final chapter.


© ClickIT DevOps & Software Development | 2015 – 2023 | All Rights Reserved
Privacy Policy · Terms of Service · Cookies Policy